GDPR is no joke: how Kloki keeps your HR data secure
The first thought when you move working time records online is usually relief: no more spreadsheets. The second is a list of questions. Where is our data? Who can open it? What if someone sees a colleague's contract or sick leave? This is how Kloki looks after your data, and why management and IT can sleep at night.
1. No looking at other people's business data
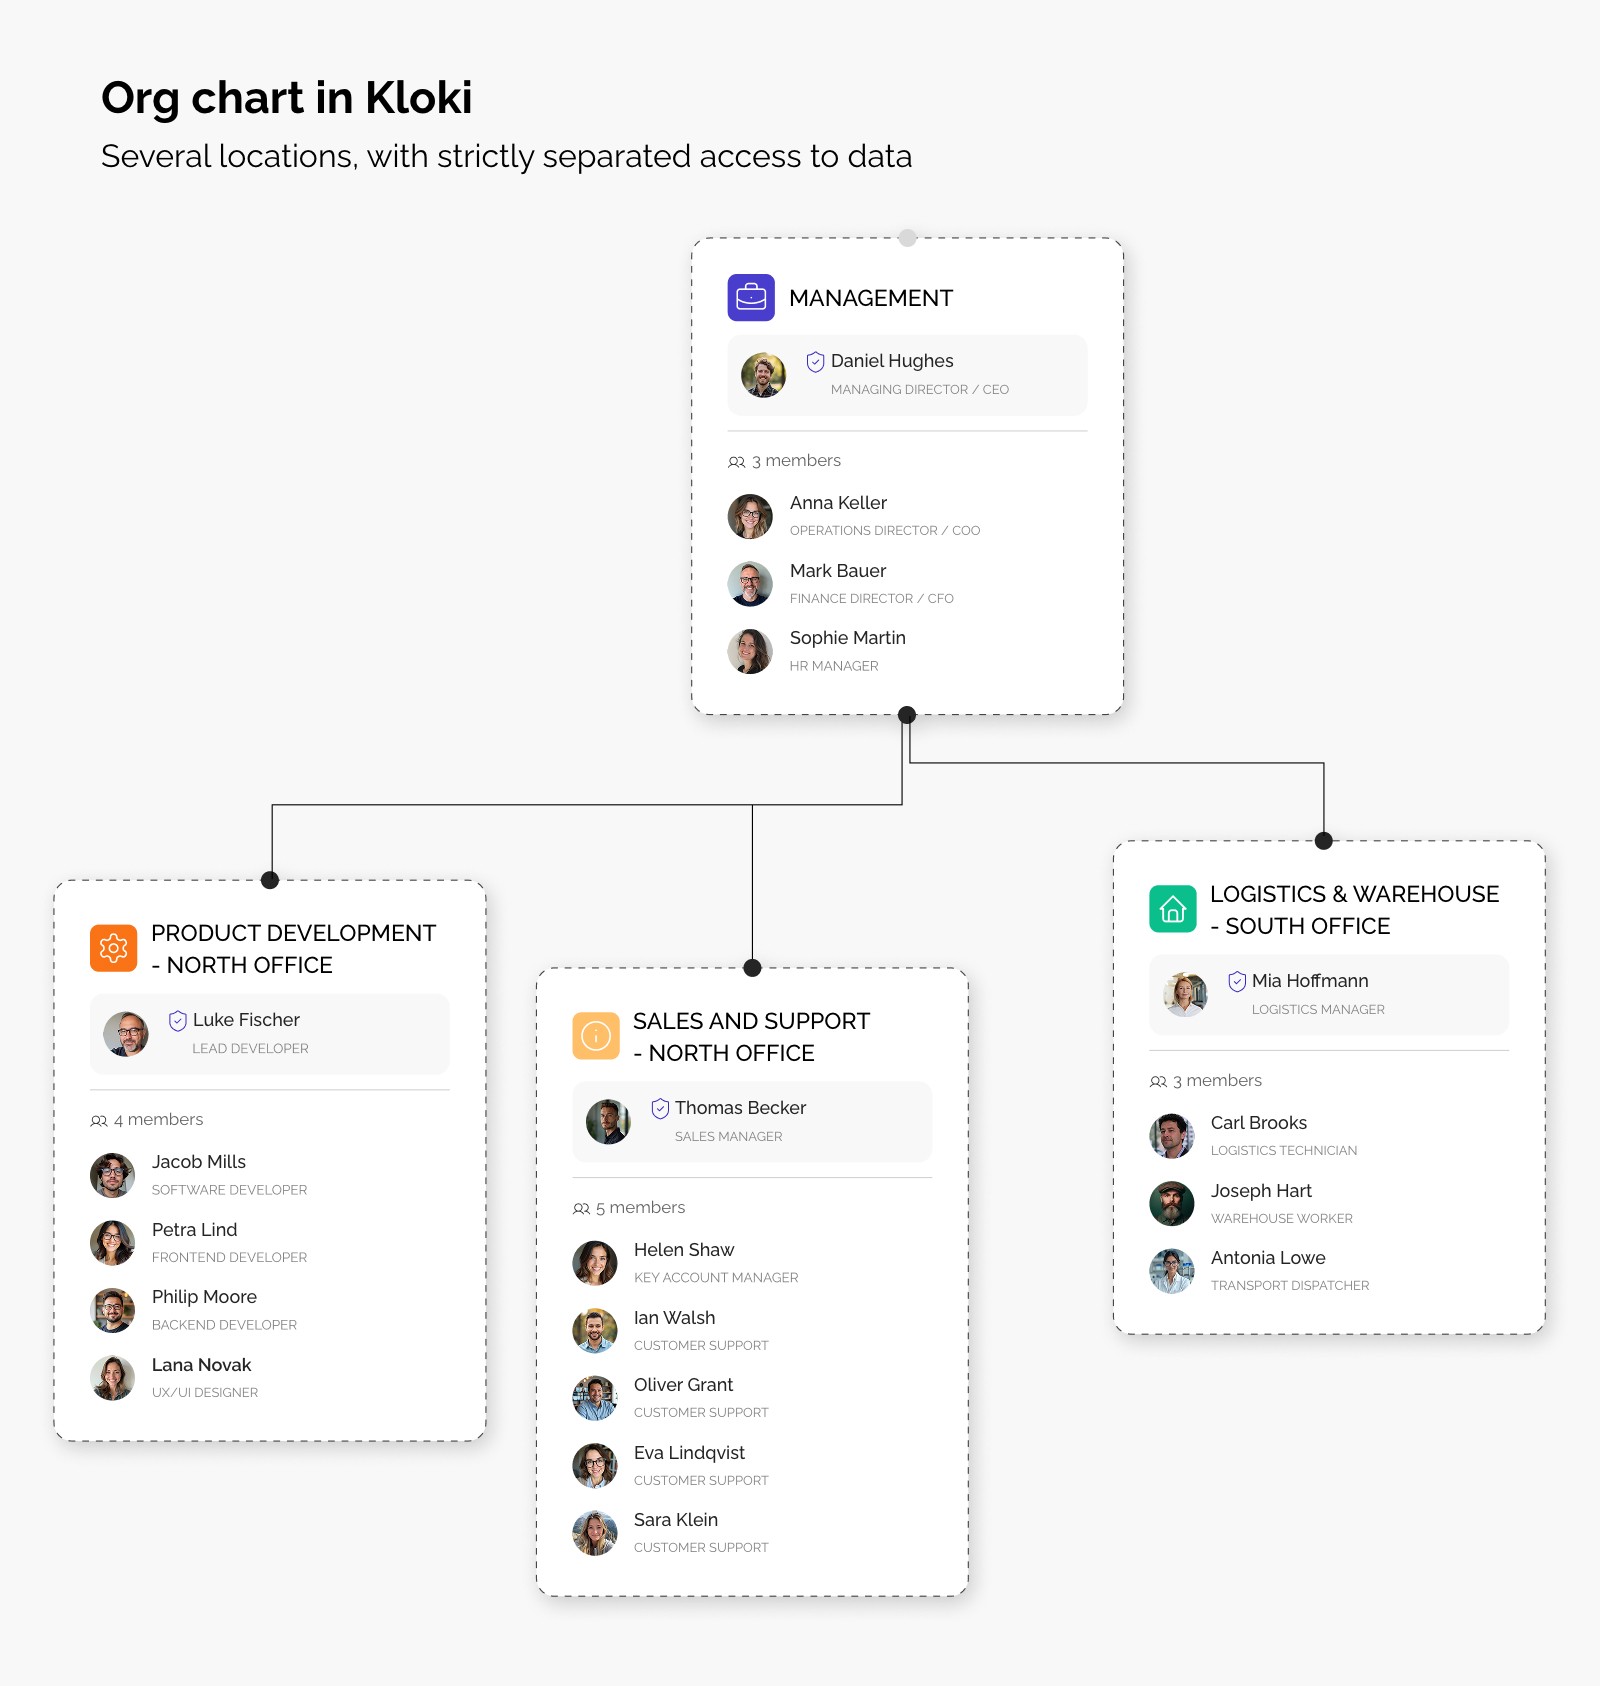
If you run several locations or several legal entities, you will ask this first: can one branch see another branch's data?
No. In Kloki, data isolation is built into the system itself, at the level of every single database query. Your branches, or the separate businesses in a group, are kept fully apart. Nothing spills over from one to another.
The warehouse team, for example, does not see the requests or documents of the sales office.
2. What happens when someone leaves
Forget switching off a dozen passwords in a dozen places. Kloki supports sign-in with Microsoft and Google accounts (SSO), passwordless sign-in with passkeys, and two-factor authentication (2FA). Disable the leaver's company Google or Microsoft account and they can no longer use it to sign in to Kloki.
3. Not even our support team sees your most sensitive documents
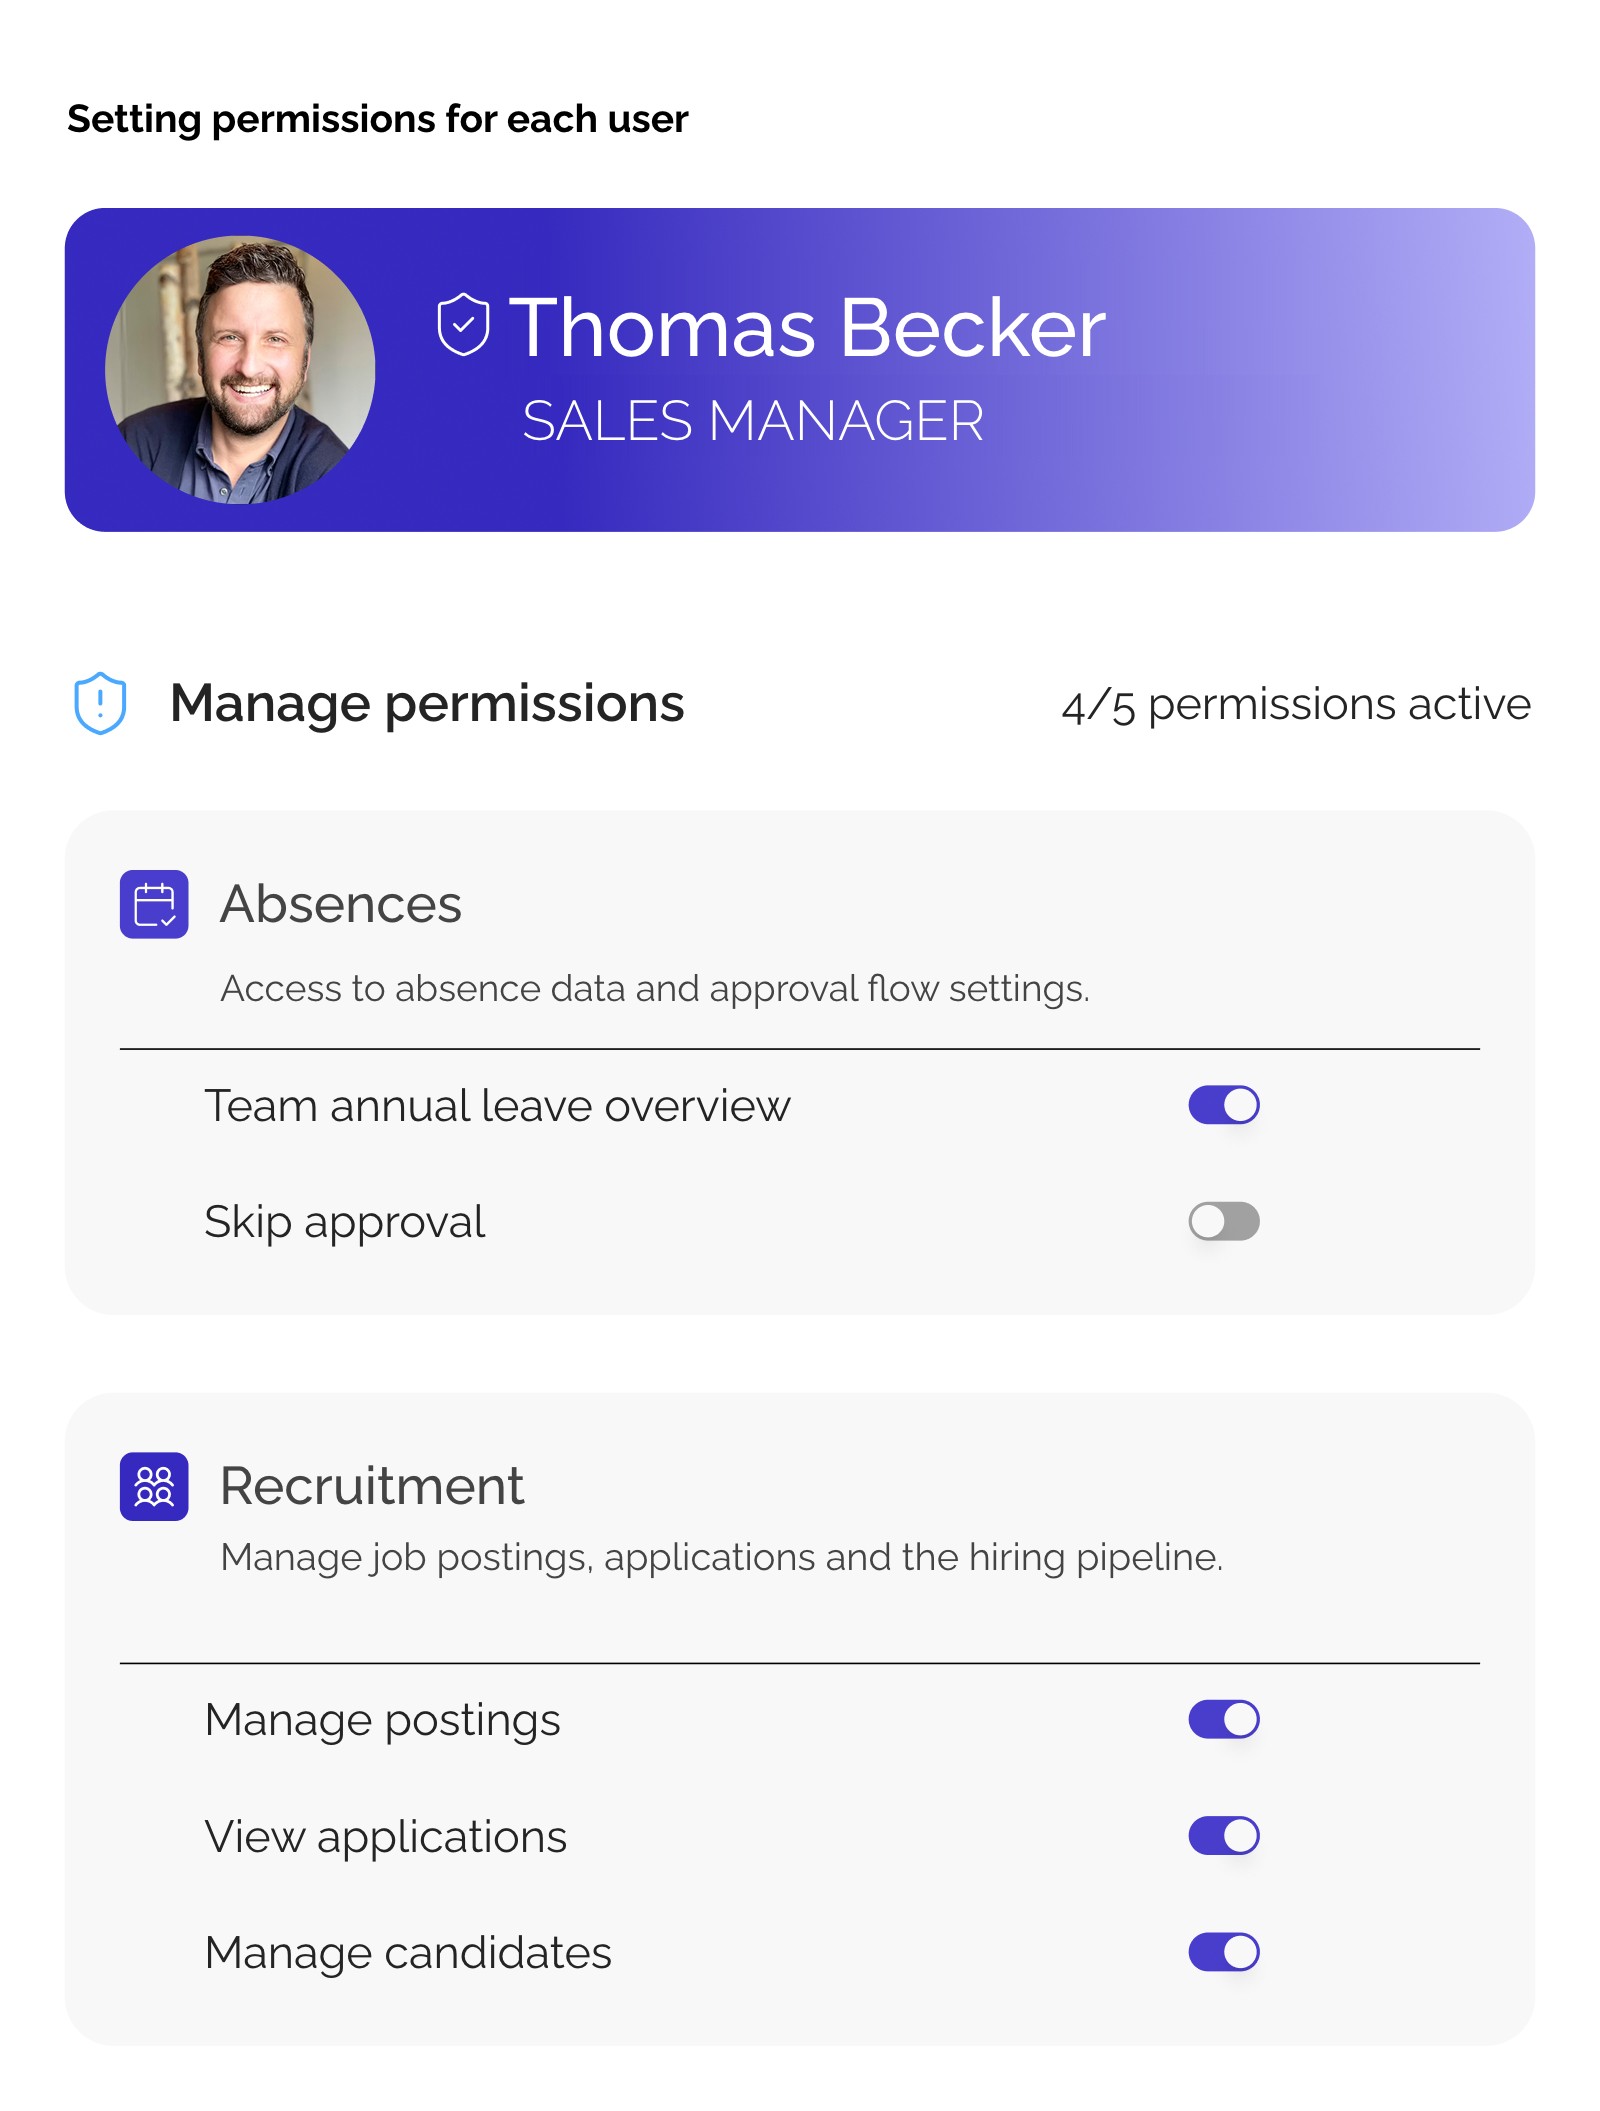
Every user sees only what they have been explicitly allowed to see. You set permissions per person and per role in detail. We went one step further.
Confidential documents such as employment contracts and health data (sick notes, for instance) are locked so tightly that our support team cannot open them even while helping you. Only the people you authorise have access.
4. Encryption and an audit trail
Kloki is built by Kodius, a team with years of experience building core systems for banks and insurers and working with health data (for IQVIA, among others) under strict HIPAA rules. That experience went into Kloki:
- Encryption in transit and at rest: data travels over TLS, and the database and backups are encrypted.
- Audit log: every opening of a confidential document and every change of permissions is recorded: who, what and when. You have a record of who did what.
- Electronic signatures: documents are signed within the EU eIDAS framework, with a second factor (an authenticator app) required for every signature.
5. So where is the data, really
If you have an IT team, server location is the first thing they will ask about. Your data is not shipped to unknown servers across the ocean. The app and the database run on servers inside the European Union, and data does not leave the EU without an adequate legal basis such as Standard Contractual Clauses (SCCs).
The right to erasure, and the rest of the GDPR
Compliance with the General Data Protection Regulation (GDPR) is not a line on paper for us. Here is how it maps to Kloki:
- Article 28: we sign a clear data processing agreement (DPA) with every customer.
- Article 32: security, confidentiality and availability of processing are built into the product.
- Article 9: special categories of data, such as health data, get extra care and the strictest access rules.
- Articles 15 to 21: you can export your data or have it permanently deleted whenever you ask.
Moving HR processes online must not put business or personal data at risk. With Kloki you get software that ends manual record keeping and saves time, and a long-term partner that protects your business to high technical and legal standards. See how this works in the document archive and time tracking, or read why Kloki.